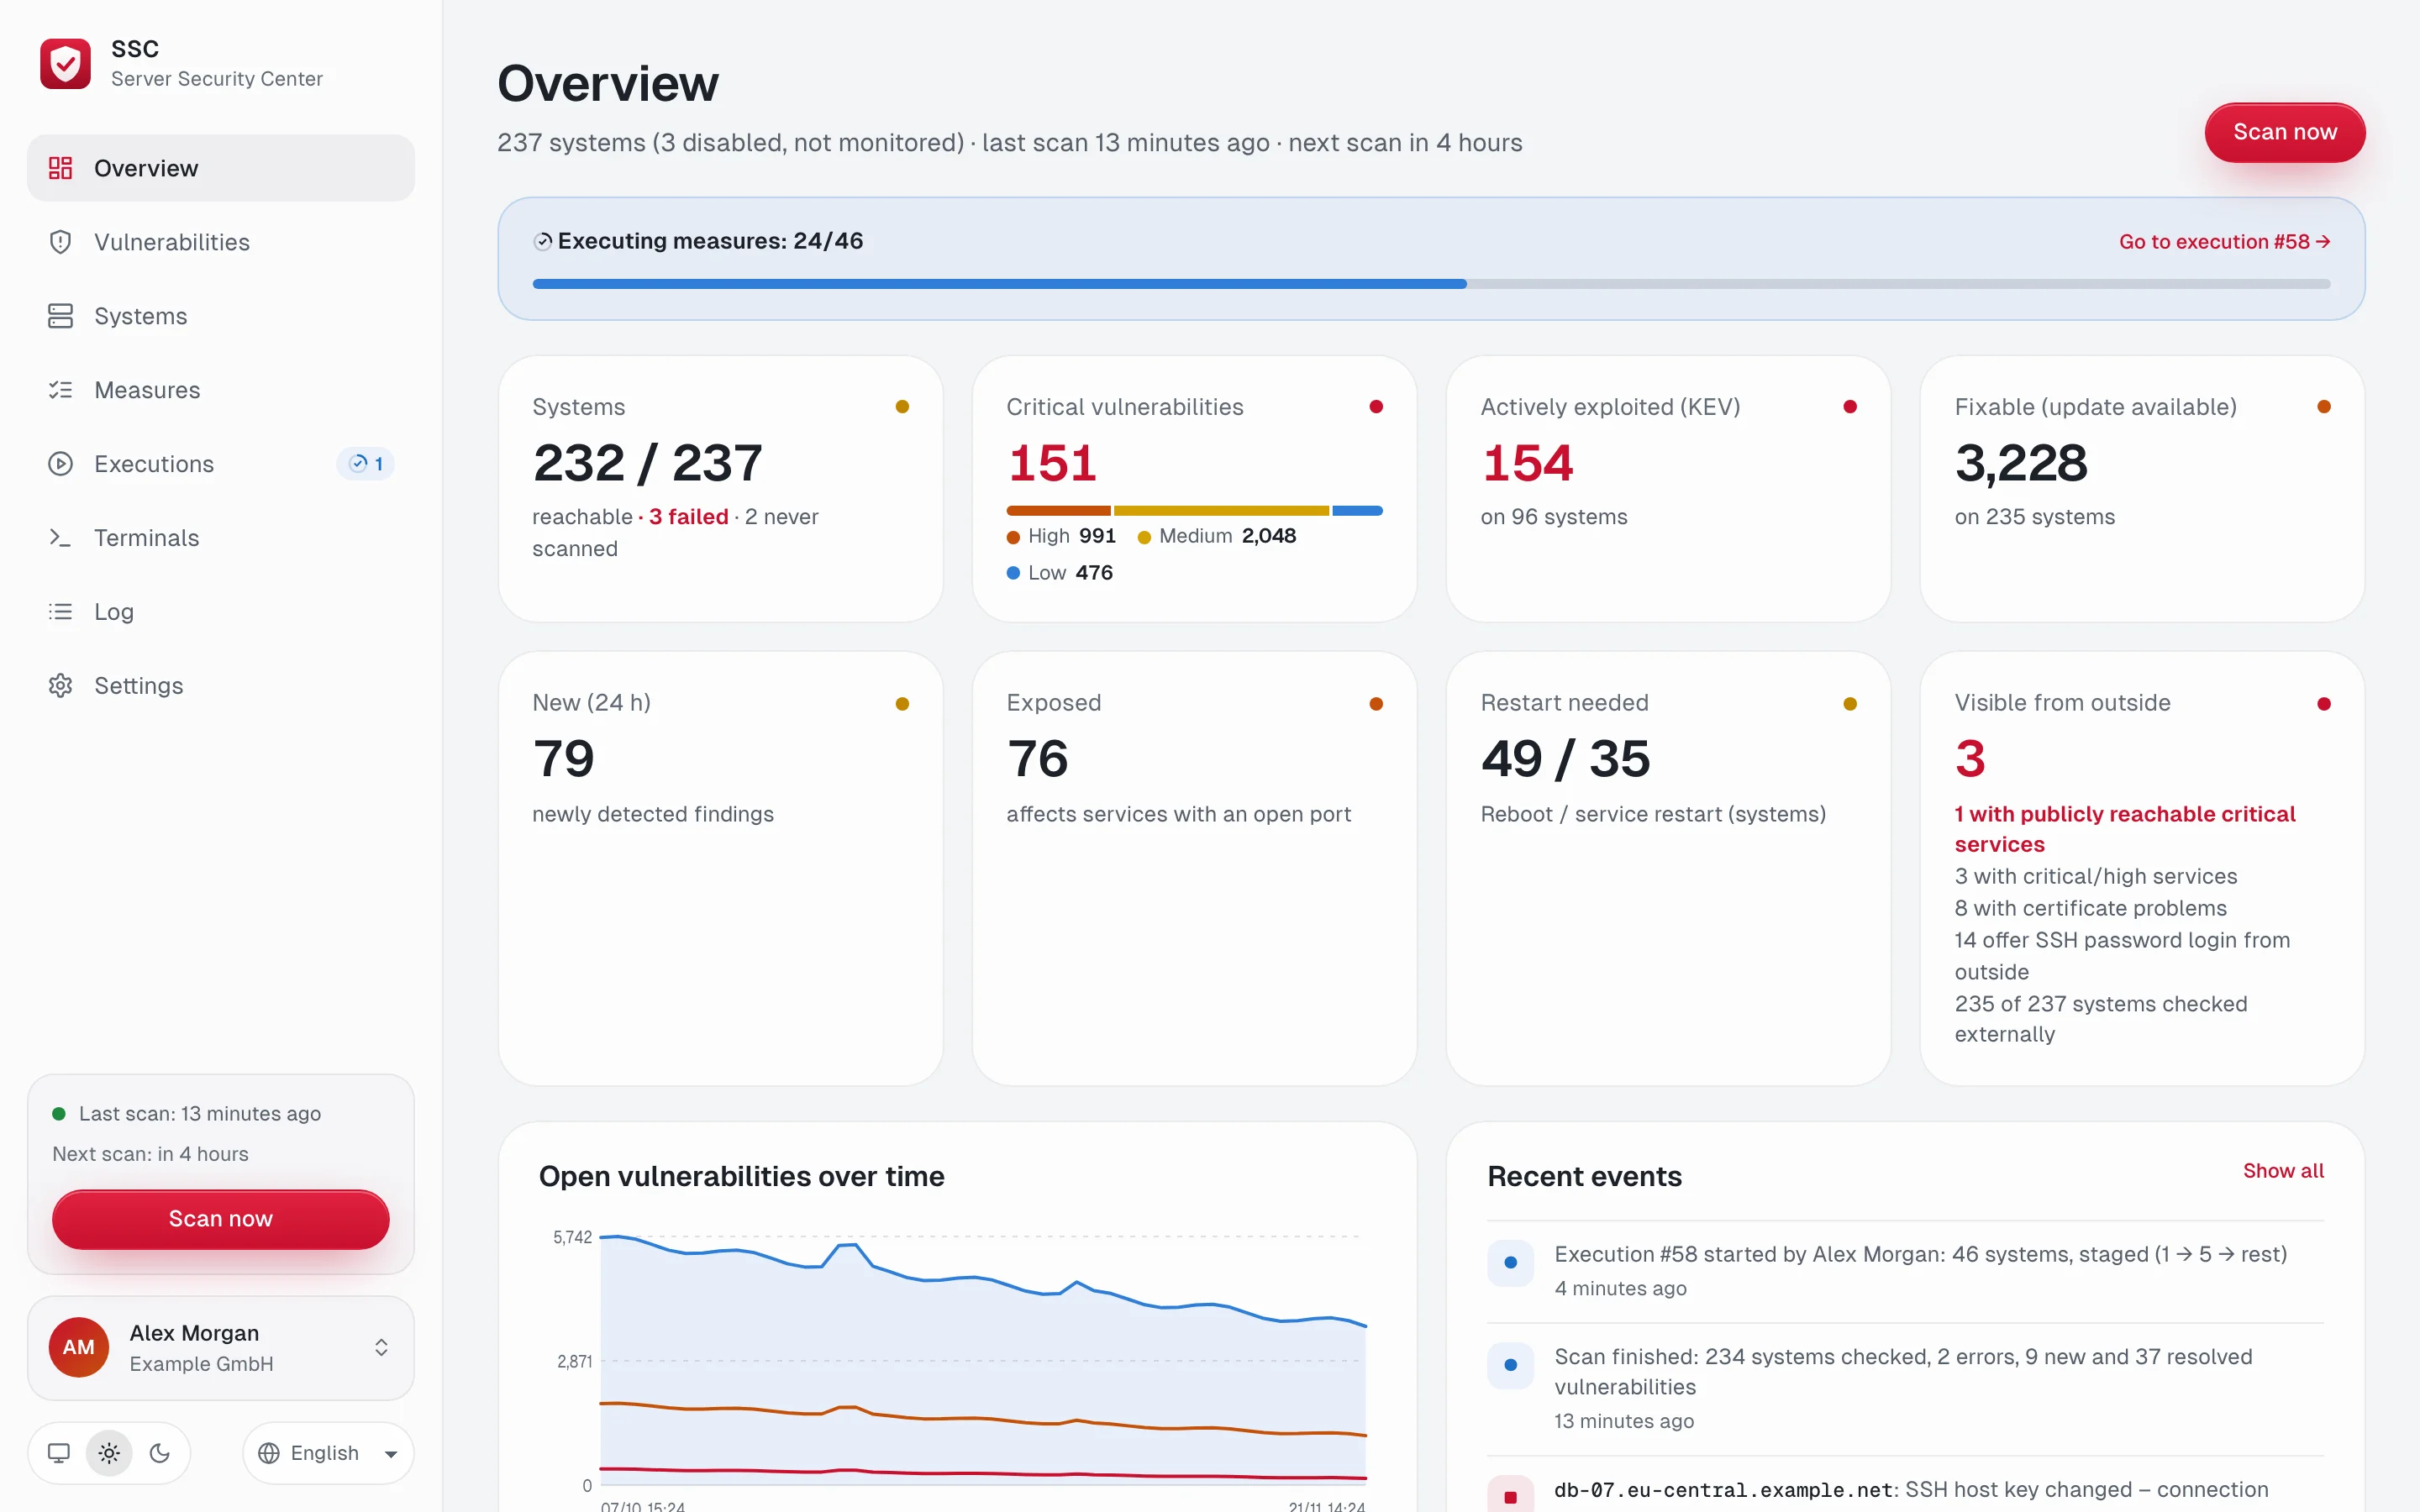
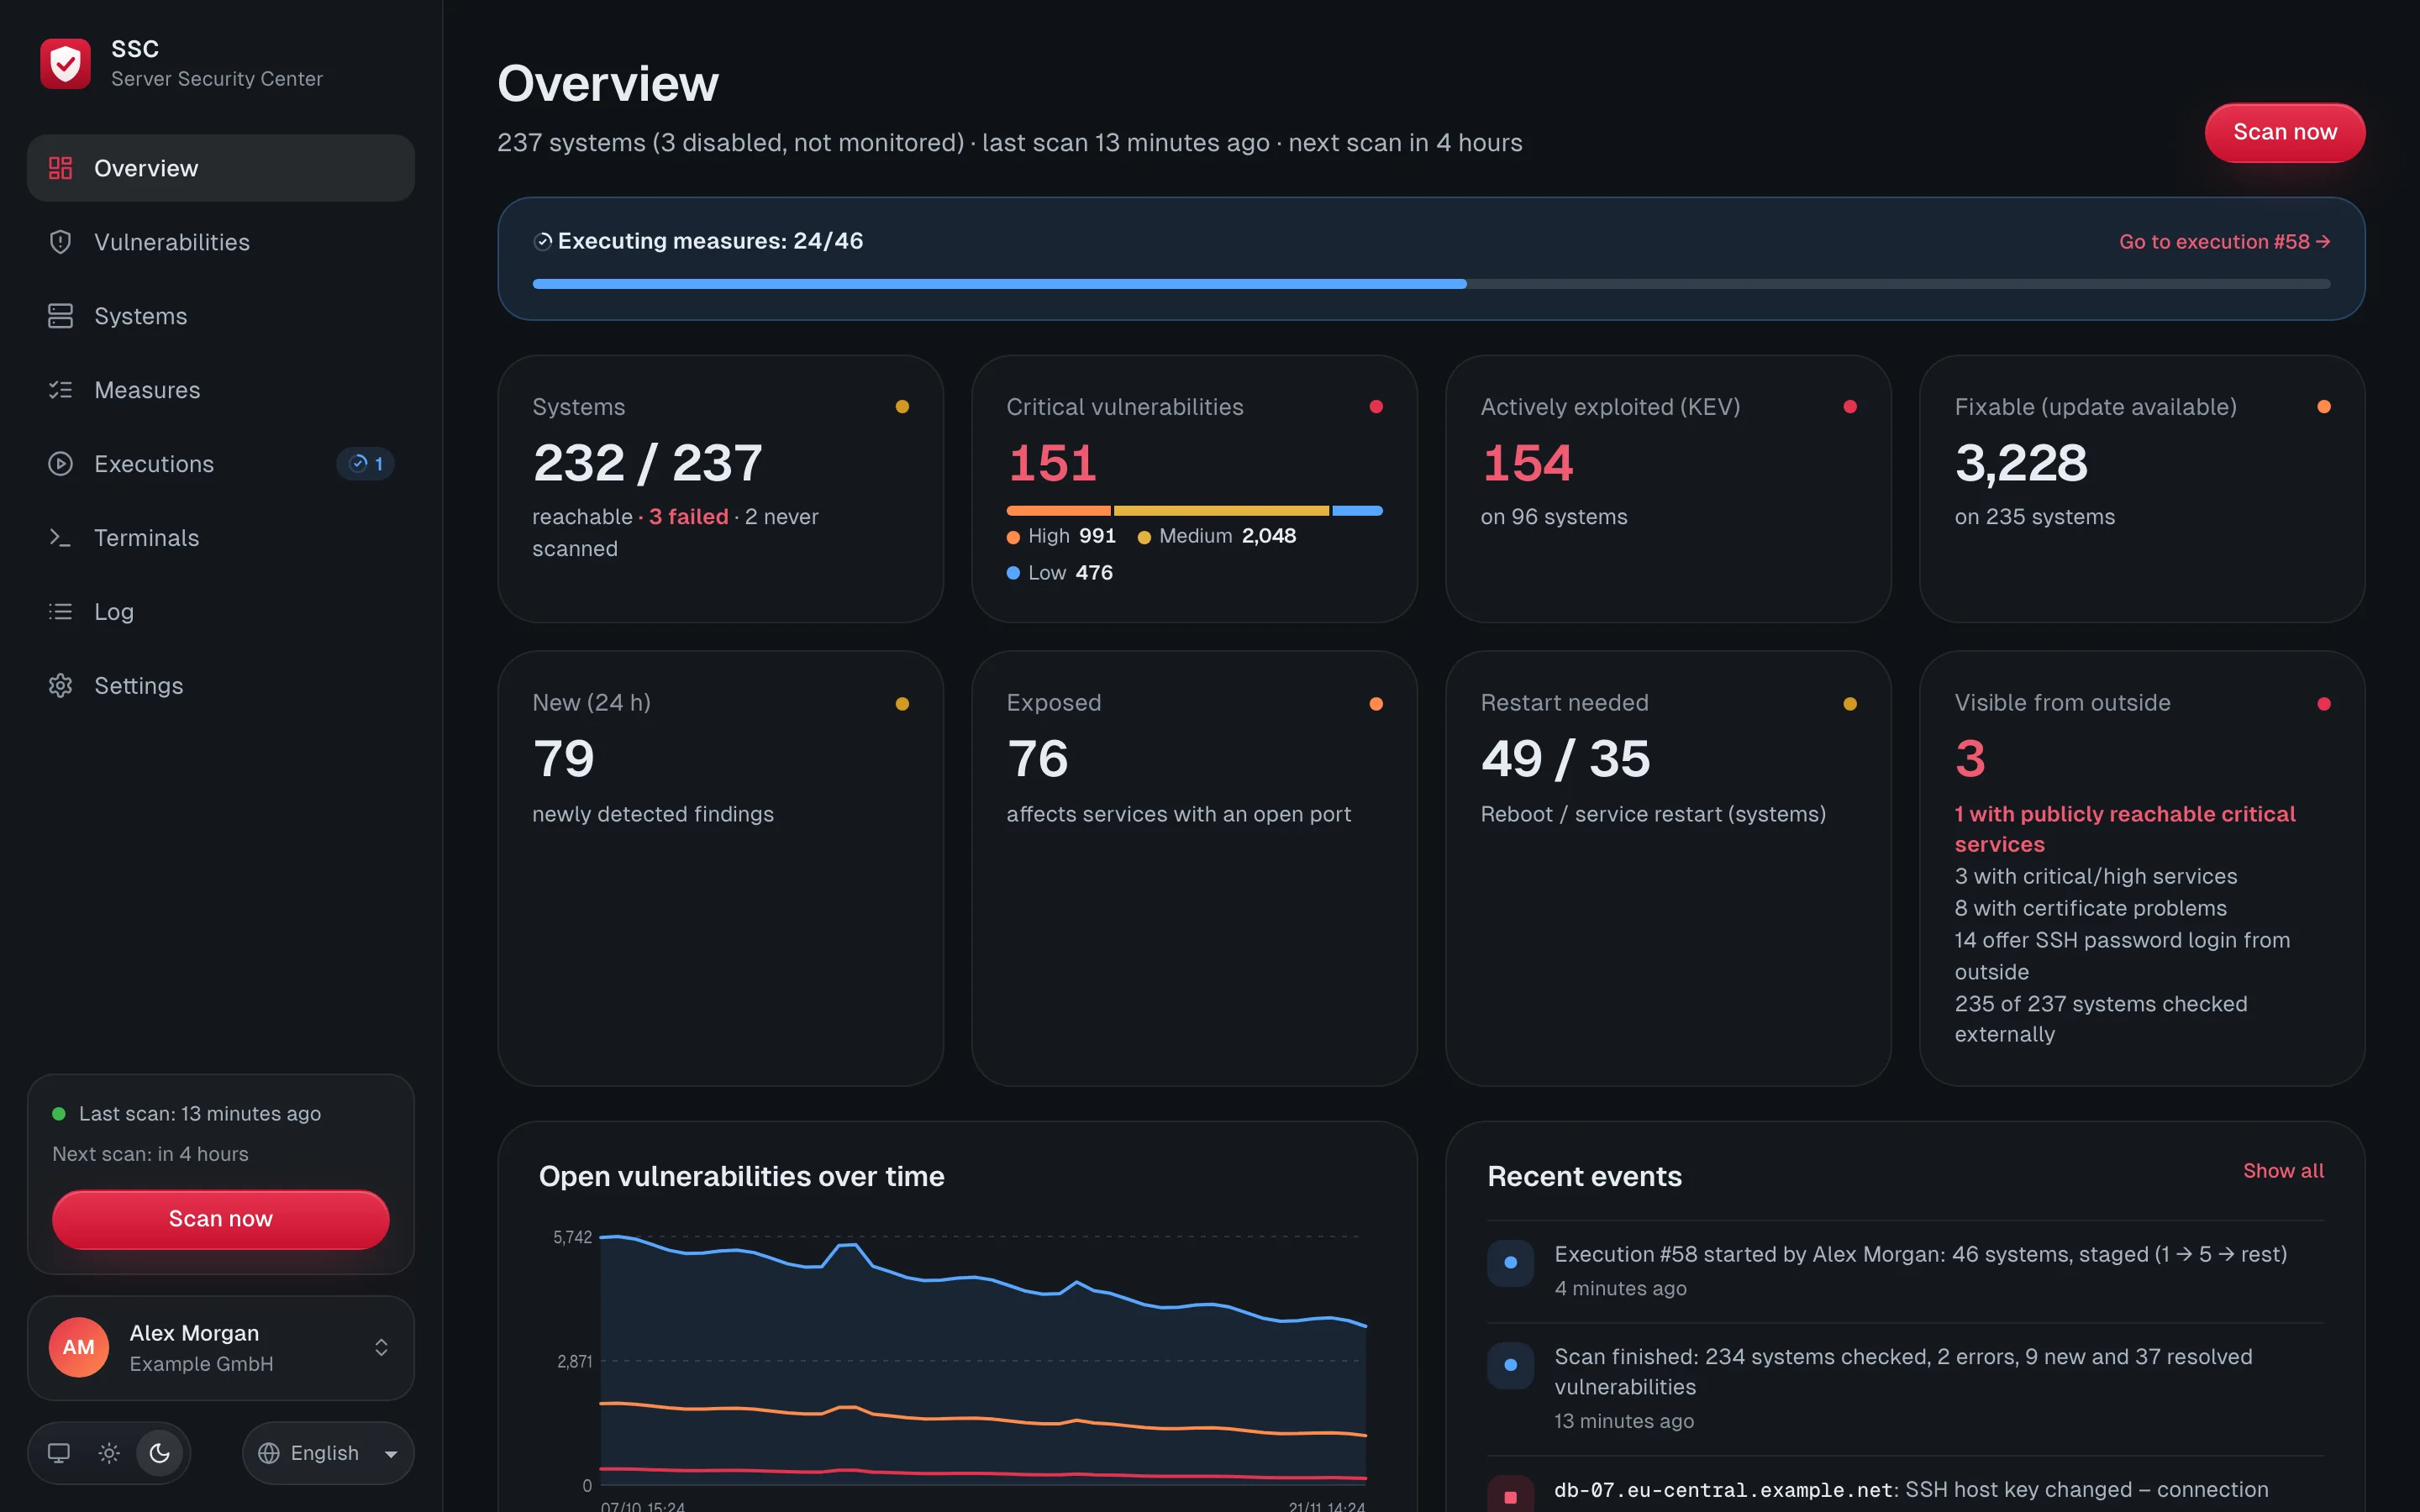
Fleet at a glance
Risk, trends and what changed since yesterday – for hundreds of servers.
CVE scanning over SSH and one-click patching for Linux fleets.
No credit card · macOS, Windows & Linux
Everything in one place
One desktop app replaces scanners, spreadsheets and SSH loops.
Risk, trends and what changed since yesterday – for hundreds of servers.
Severity, CISA KEV, EPSS and public exposure merged into one 0–100 score.
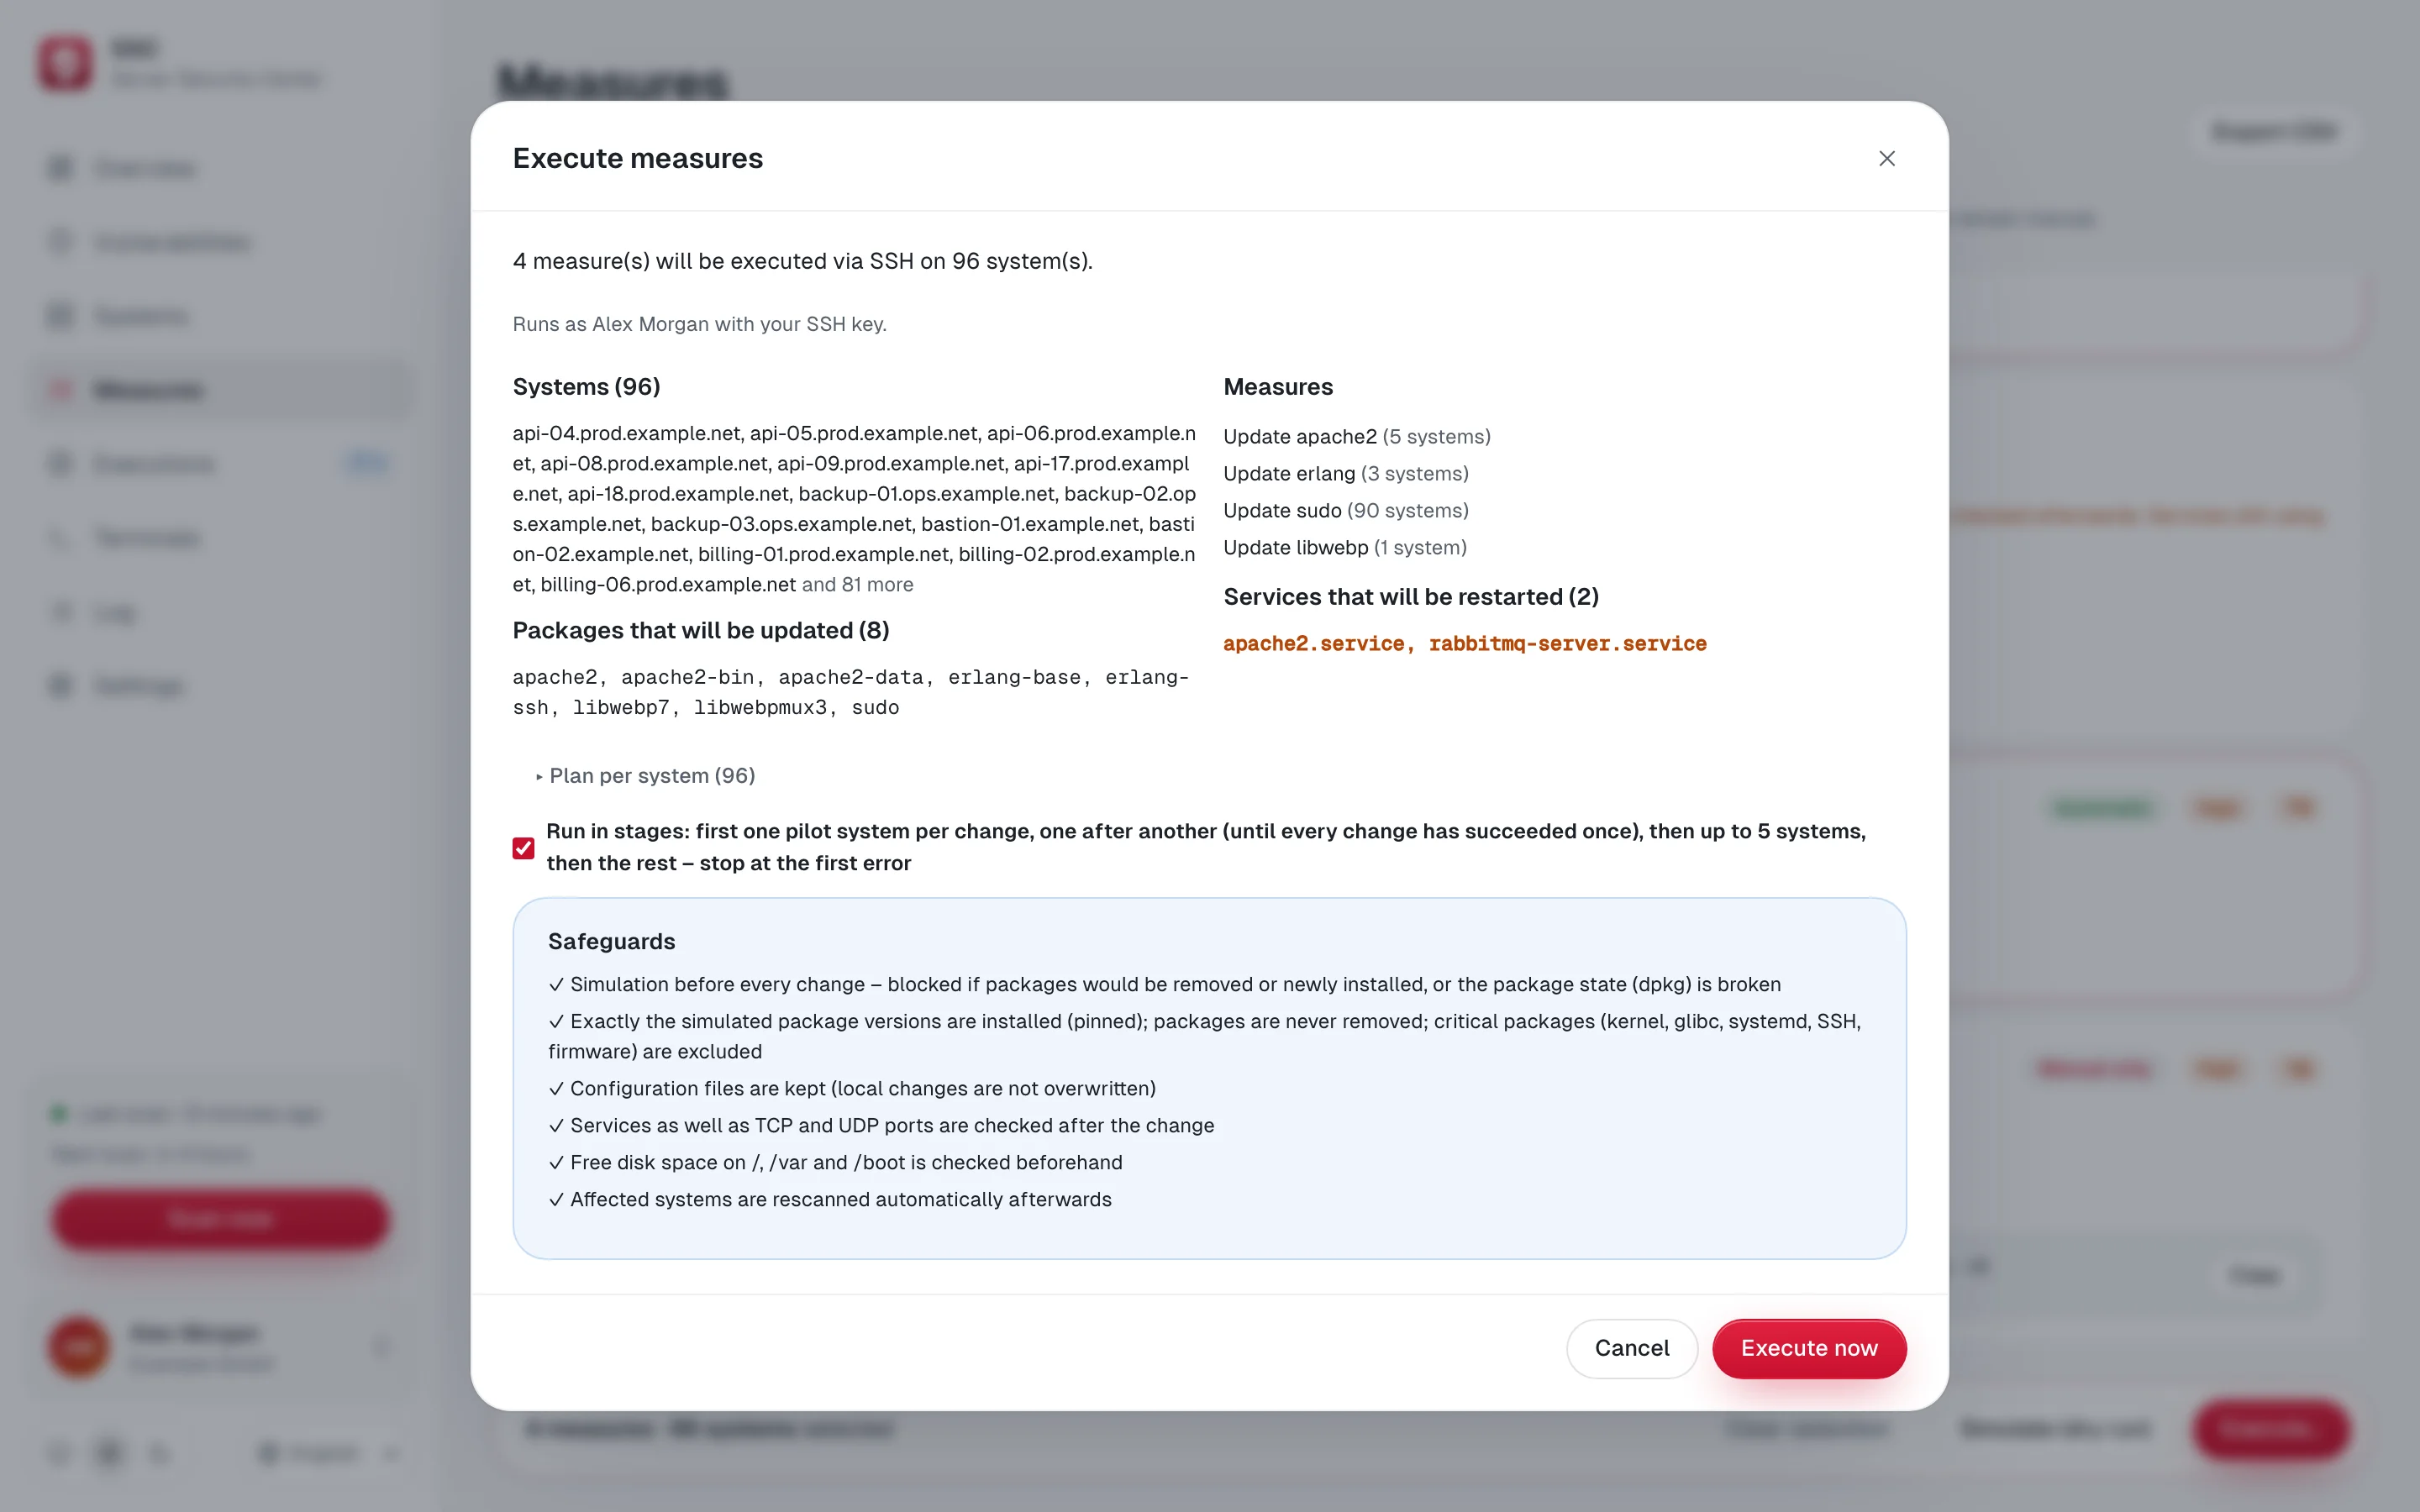
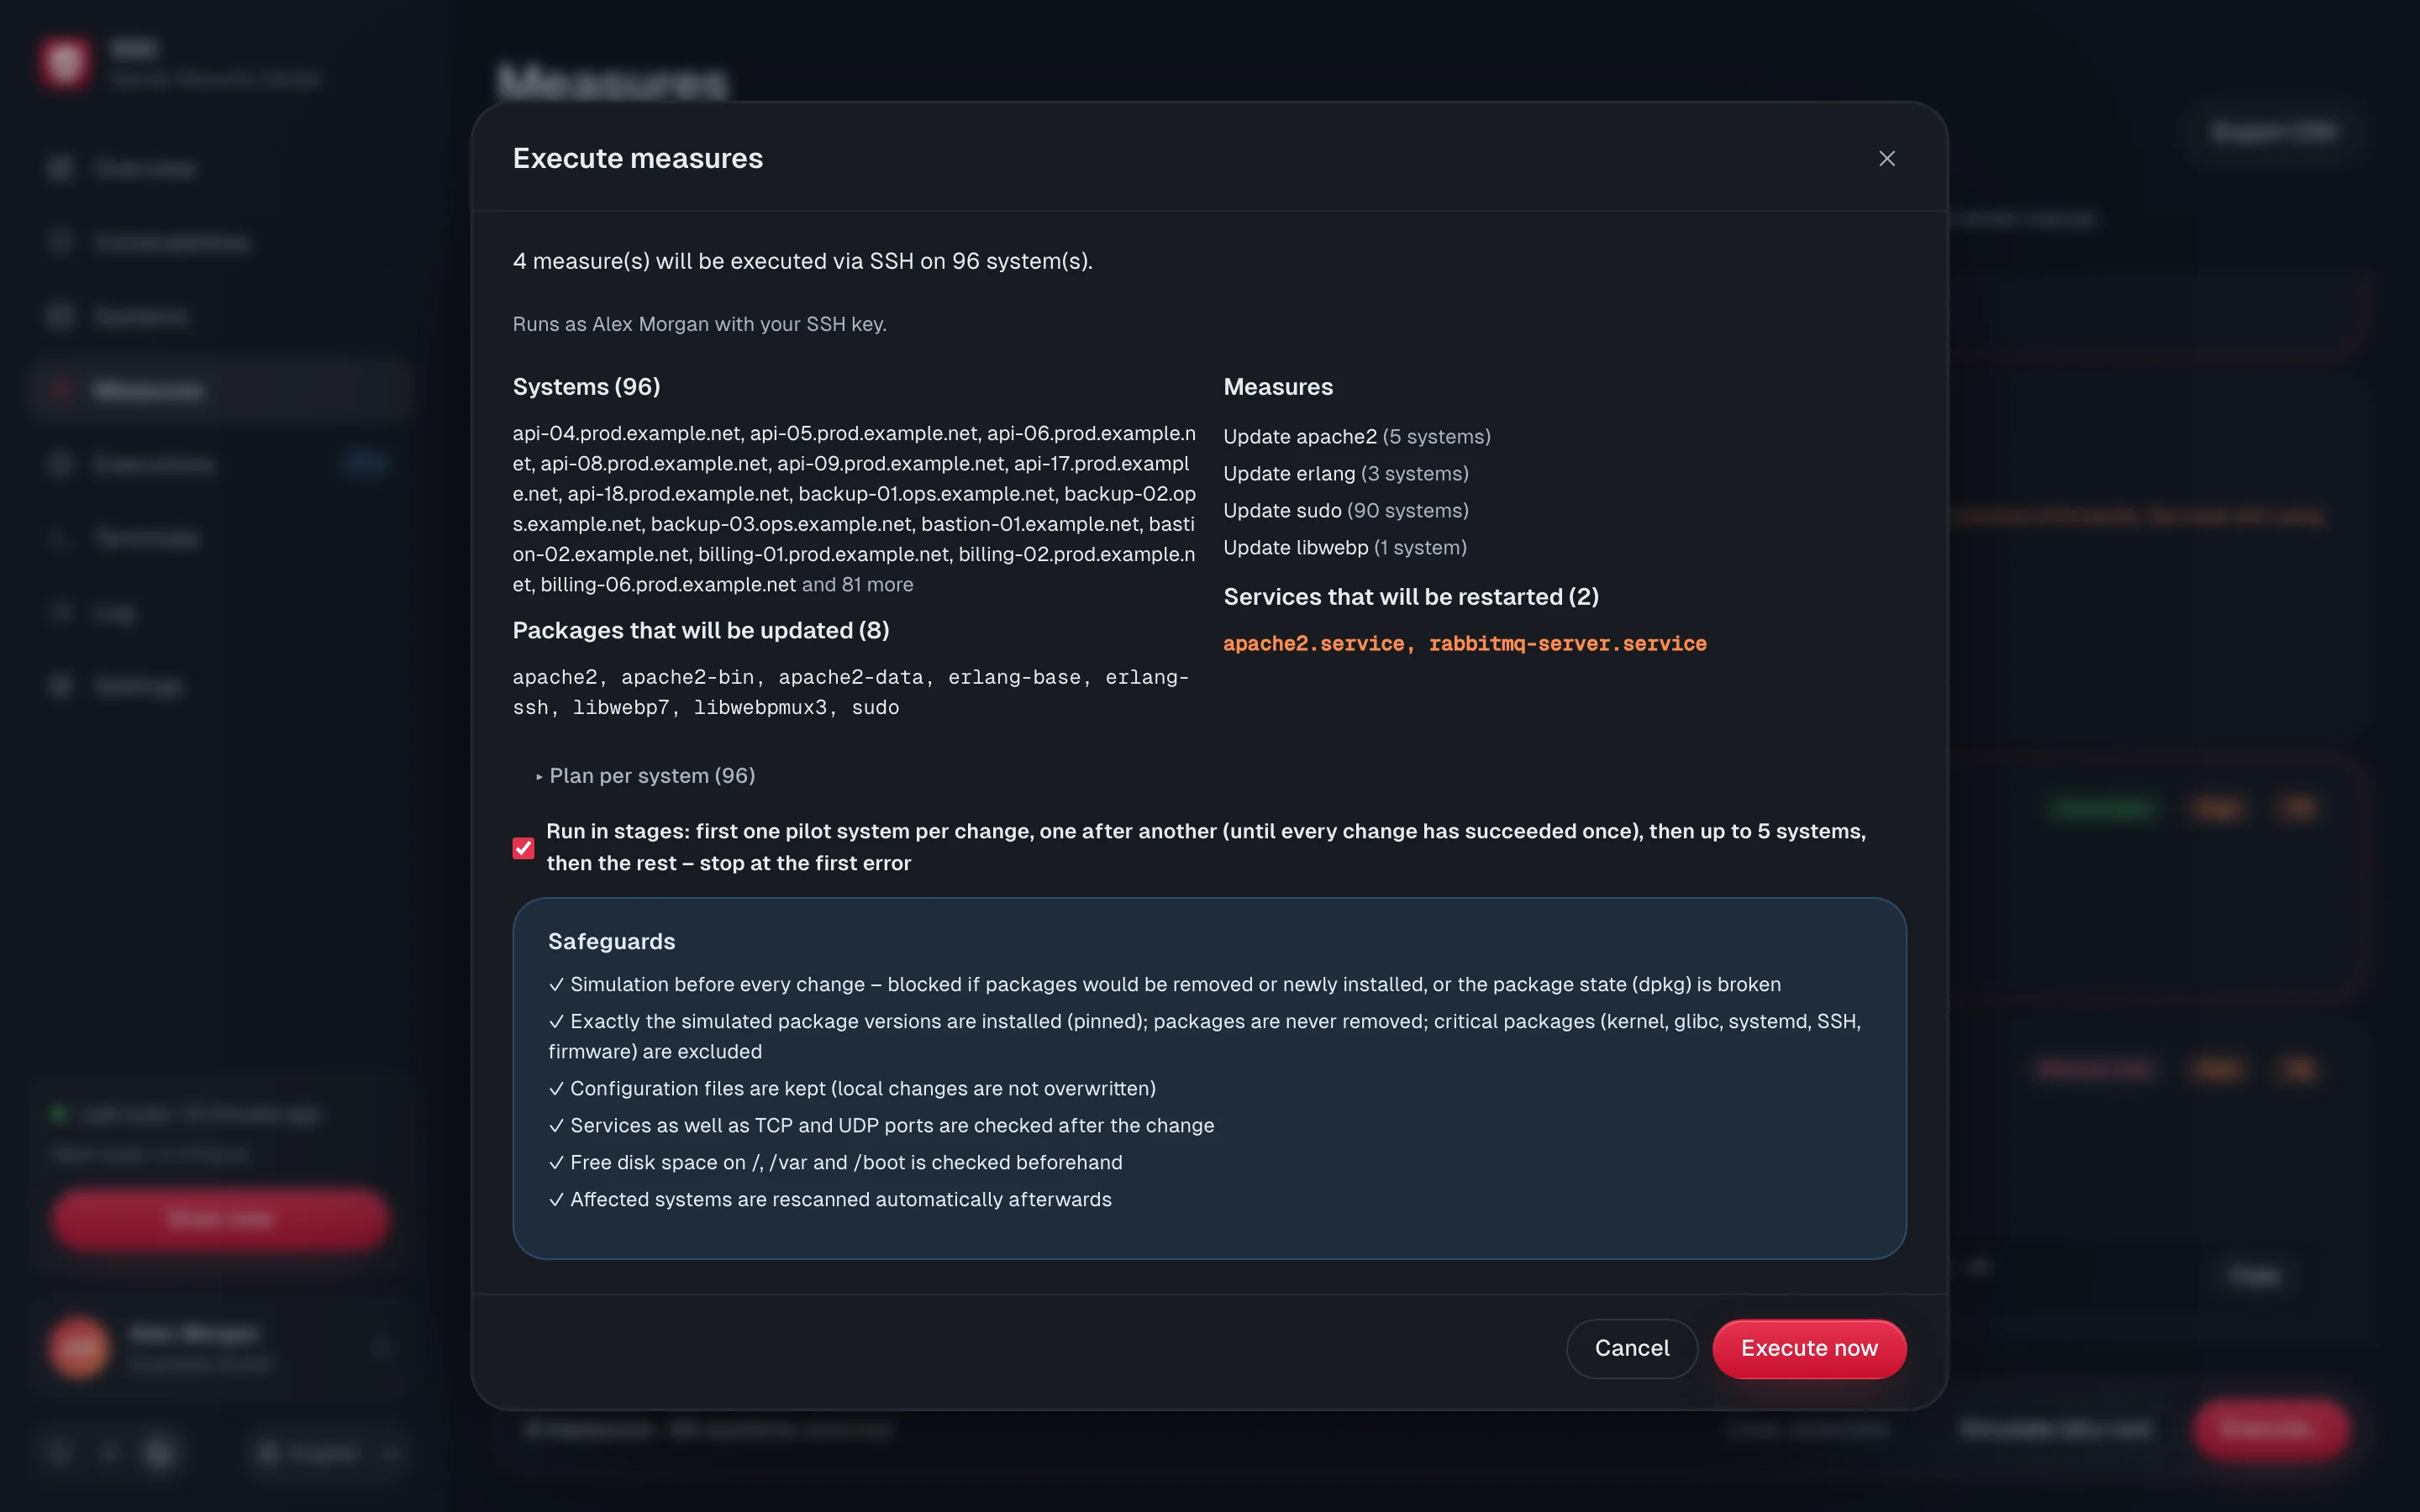
Simulate, then roll out in stages with canaries. Risky changes stay manual.
Open ports, TLS, headers and SSH login methods – exactly what attackers see.
Spots password and root logins and switches them to key-only.
# sshd -T
- passwordauthentication yes
+ passwordauthentication no
- permitrootlogin yes
+ permitrootlogin prohibit-password
Desktop and e-mail alerts for CVEs above your severity threshold or actively exploited, changed host or agent keys, unreachable systems and failed scans. SSC starts in the tray when you sign in, so alerts continue after a reboot.
pip, npm, Composer, JARs (log4j), gems and running containers.
Supported, LTS, ESM or end-of-life – with upgrade measures.
Take the tour
Fleet risk, trends and the most urgent work – live.
How it works
 1
Import hosts and add your SSH key. The first scan starts right away.
 2
Packages, kernels, containers and apps are matched against live CVE data.
 3
Pick measures, simulate, and roll out in safe stages – fleet-wide or per server.
Powered by the sources security teams trust
Security by design
SSC runs on your computer. No SSC cloud, no inventory upload, no inbound ports.
Scans only read. Changes happen only when you execute a measure.
Inventory and findings stay in a local database on your device.
Only anonymous package names and versions are queried – no hosts, no IPs.
Changed SSH host keys raise a critical alert instead of silently connecting.
Everywhere you work
Small, fast, auto-updating. One license, up to 3 devices per user.
Pricing
Per user, first 50 servers included. 14 days free.
€108 per user, billed yearly
Peak managed servers per billing period.
No credit card. · Trial includes everything. · Prices excl. VAT.
Need 50+ users, invoicing or a custom agreement? Talk to us
SSC connects over SSH with your key. Scans run a read-only script; the signed SSC agent adds continuous metric history – no open port, no outbound connections. Fixes run only when you execute a measure.
Ubuntu and Debian (incl. derivatives) with full package matching, plus application dependencies (pip, npm, Composer, Maven/JAR, gems) and Docker/Podman containers.
On your computer, in a local database. Only anonymous package names and versions are sent to OSV.dev – never host names or IP addresses.
A user is one person in your team, with up to 3 devices. The first 50 servers per team are included; above that a fleet fee applies, based on the peak number of managed servers per billing period. Prices are the same in euros and US dollars.
Your trial runs 14 days with every feature, up to 10 users and no credit card. Subscribe anytime; remaining trial days stay free.
Yes. Change users or cancel in the billing portal. Your plan stays active until the end of the paid period.
Yes. Every payment comes with a proper invoice. Enter your VAT ID at checkout for reverse charge within the EU.
Start your 14-day free trial – set up in five minutes.